
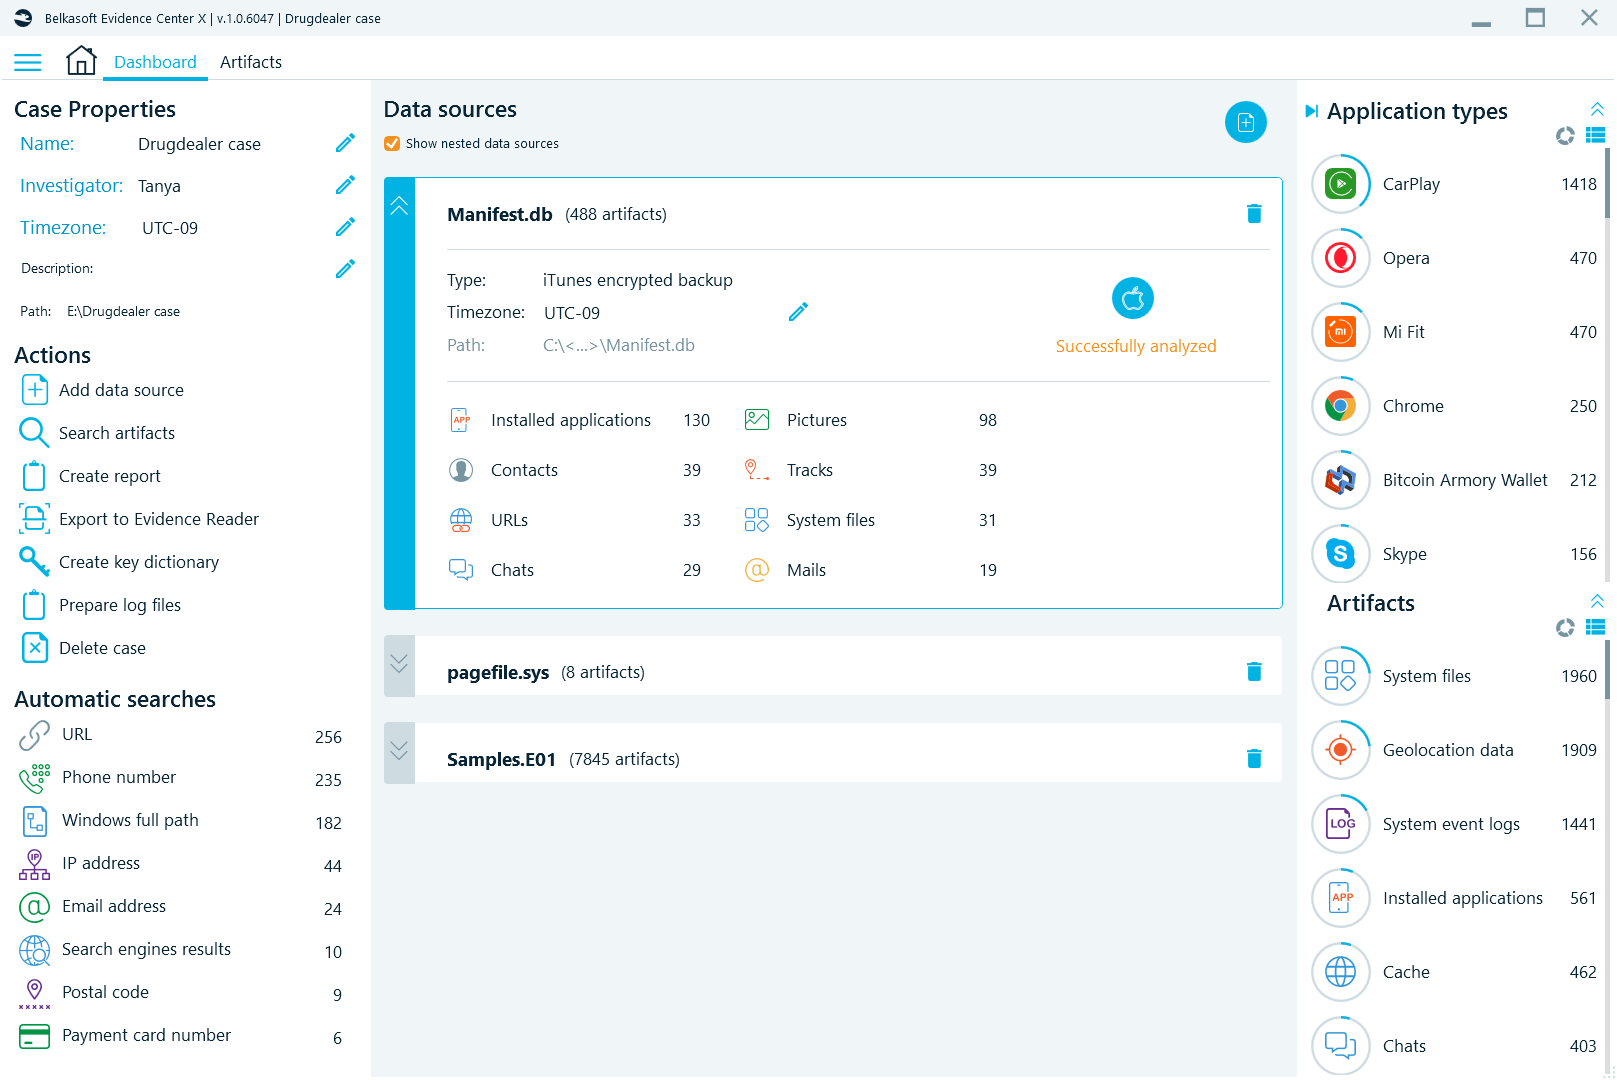
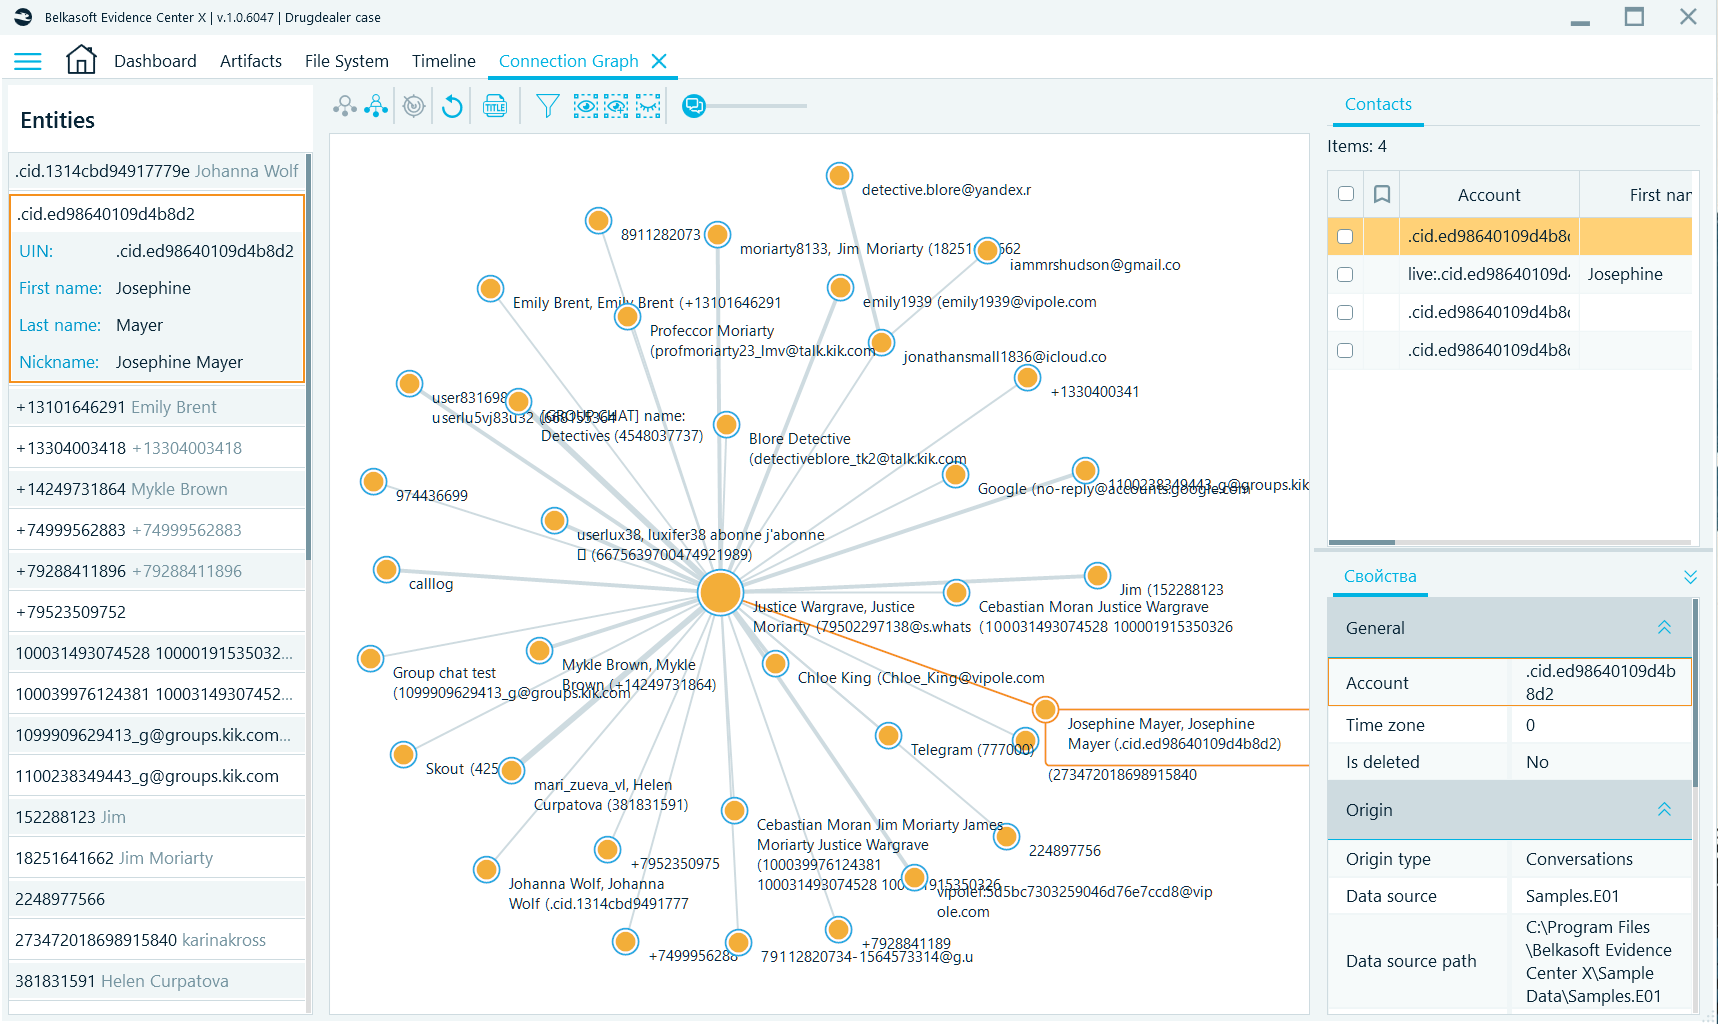
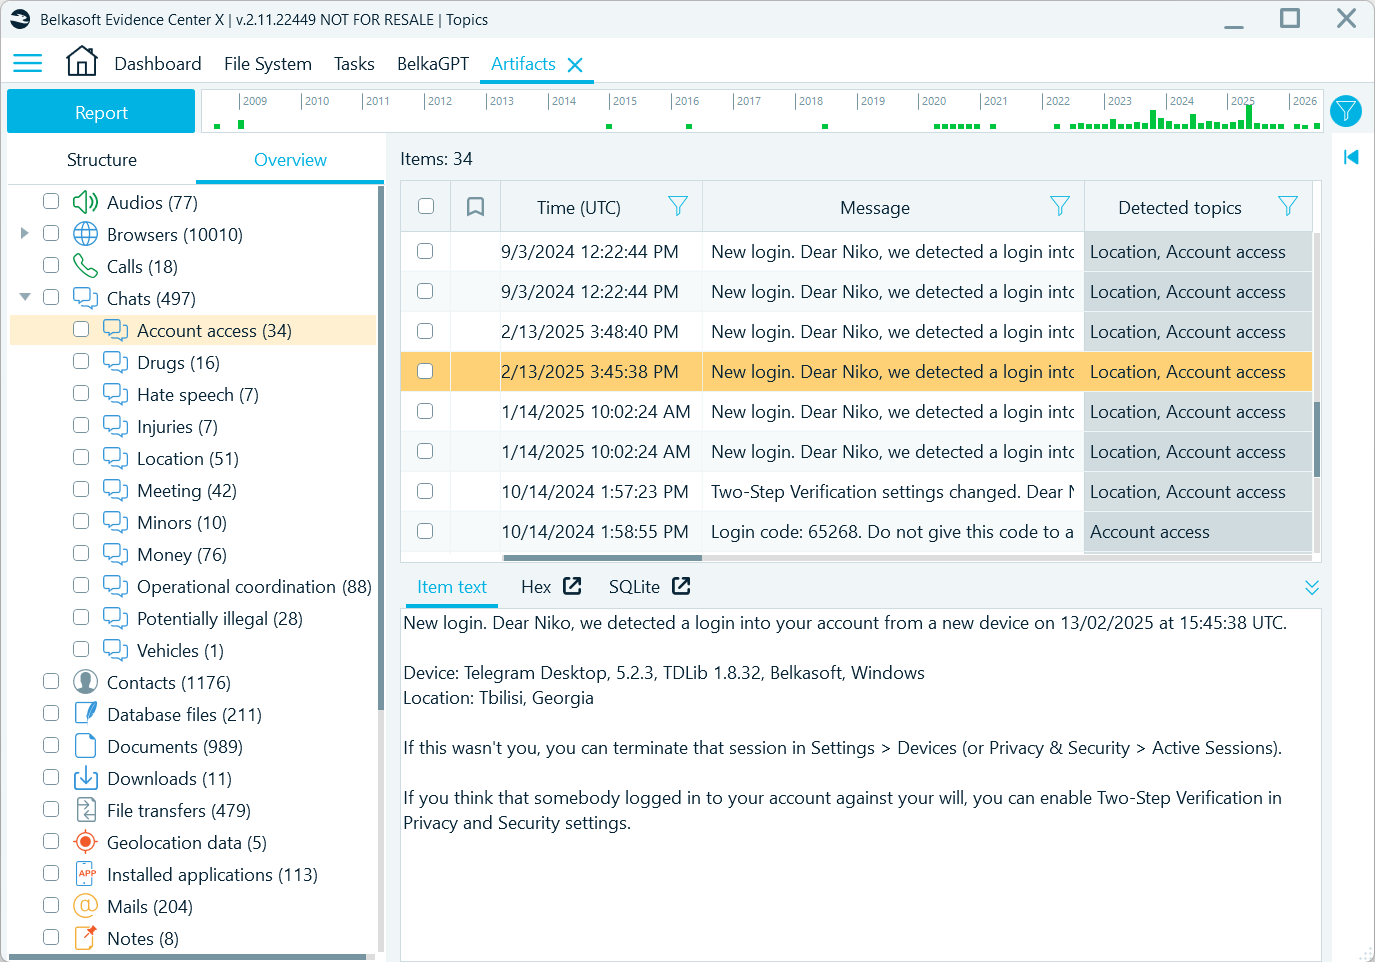
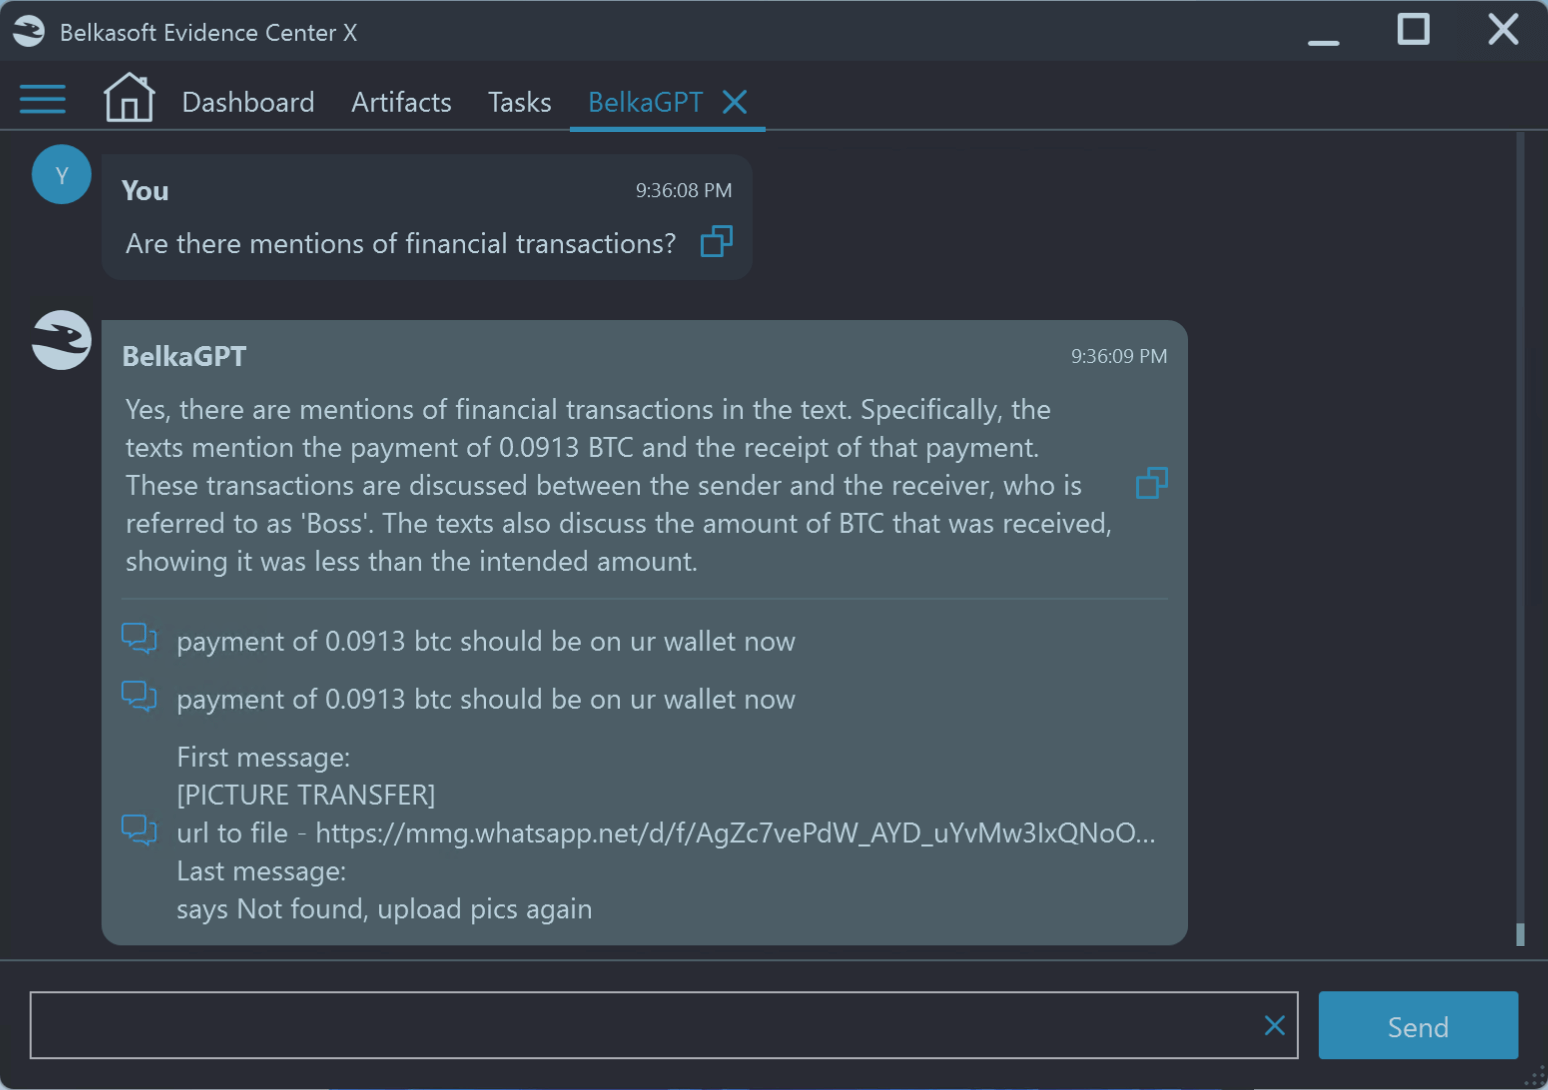
Belkasoft X Forensic
Preis auf Anfrage
Tax excluded. Shipping calculated at checkout
Belkasoft X Forensic
Sale price€0,00 EUR
Technical specifications
Here you will find the most important technical data about the product. If you have any questions, you can always contact our customer service.
CPU
network
Storage
R.A.M.
extension
console port
USB ports
LEDs
Other
form factor
cooling
Vicinity
power consumption
certificates
support
Advantages of the Belkasoft X Forensic
