MEFF M3-PRO

Sale price€10.749,00 EUR

Tax excluded. Shipping calculated at checkout

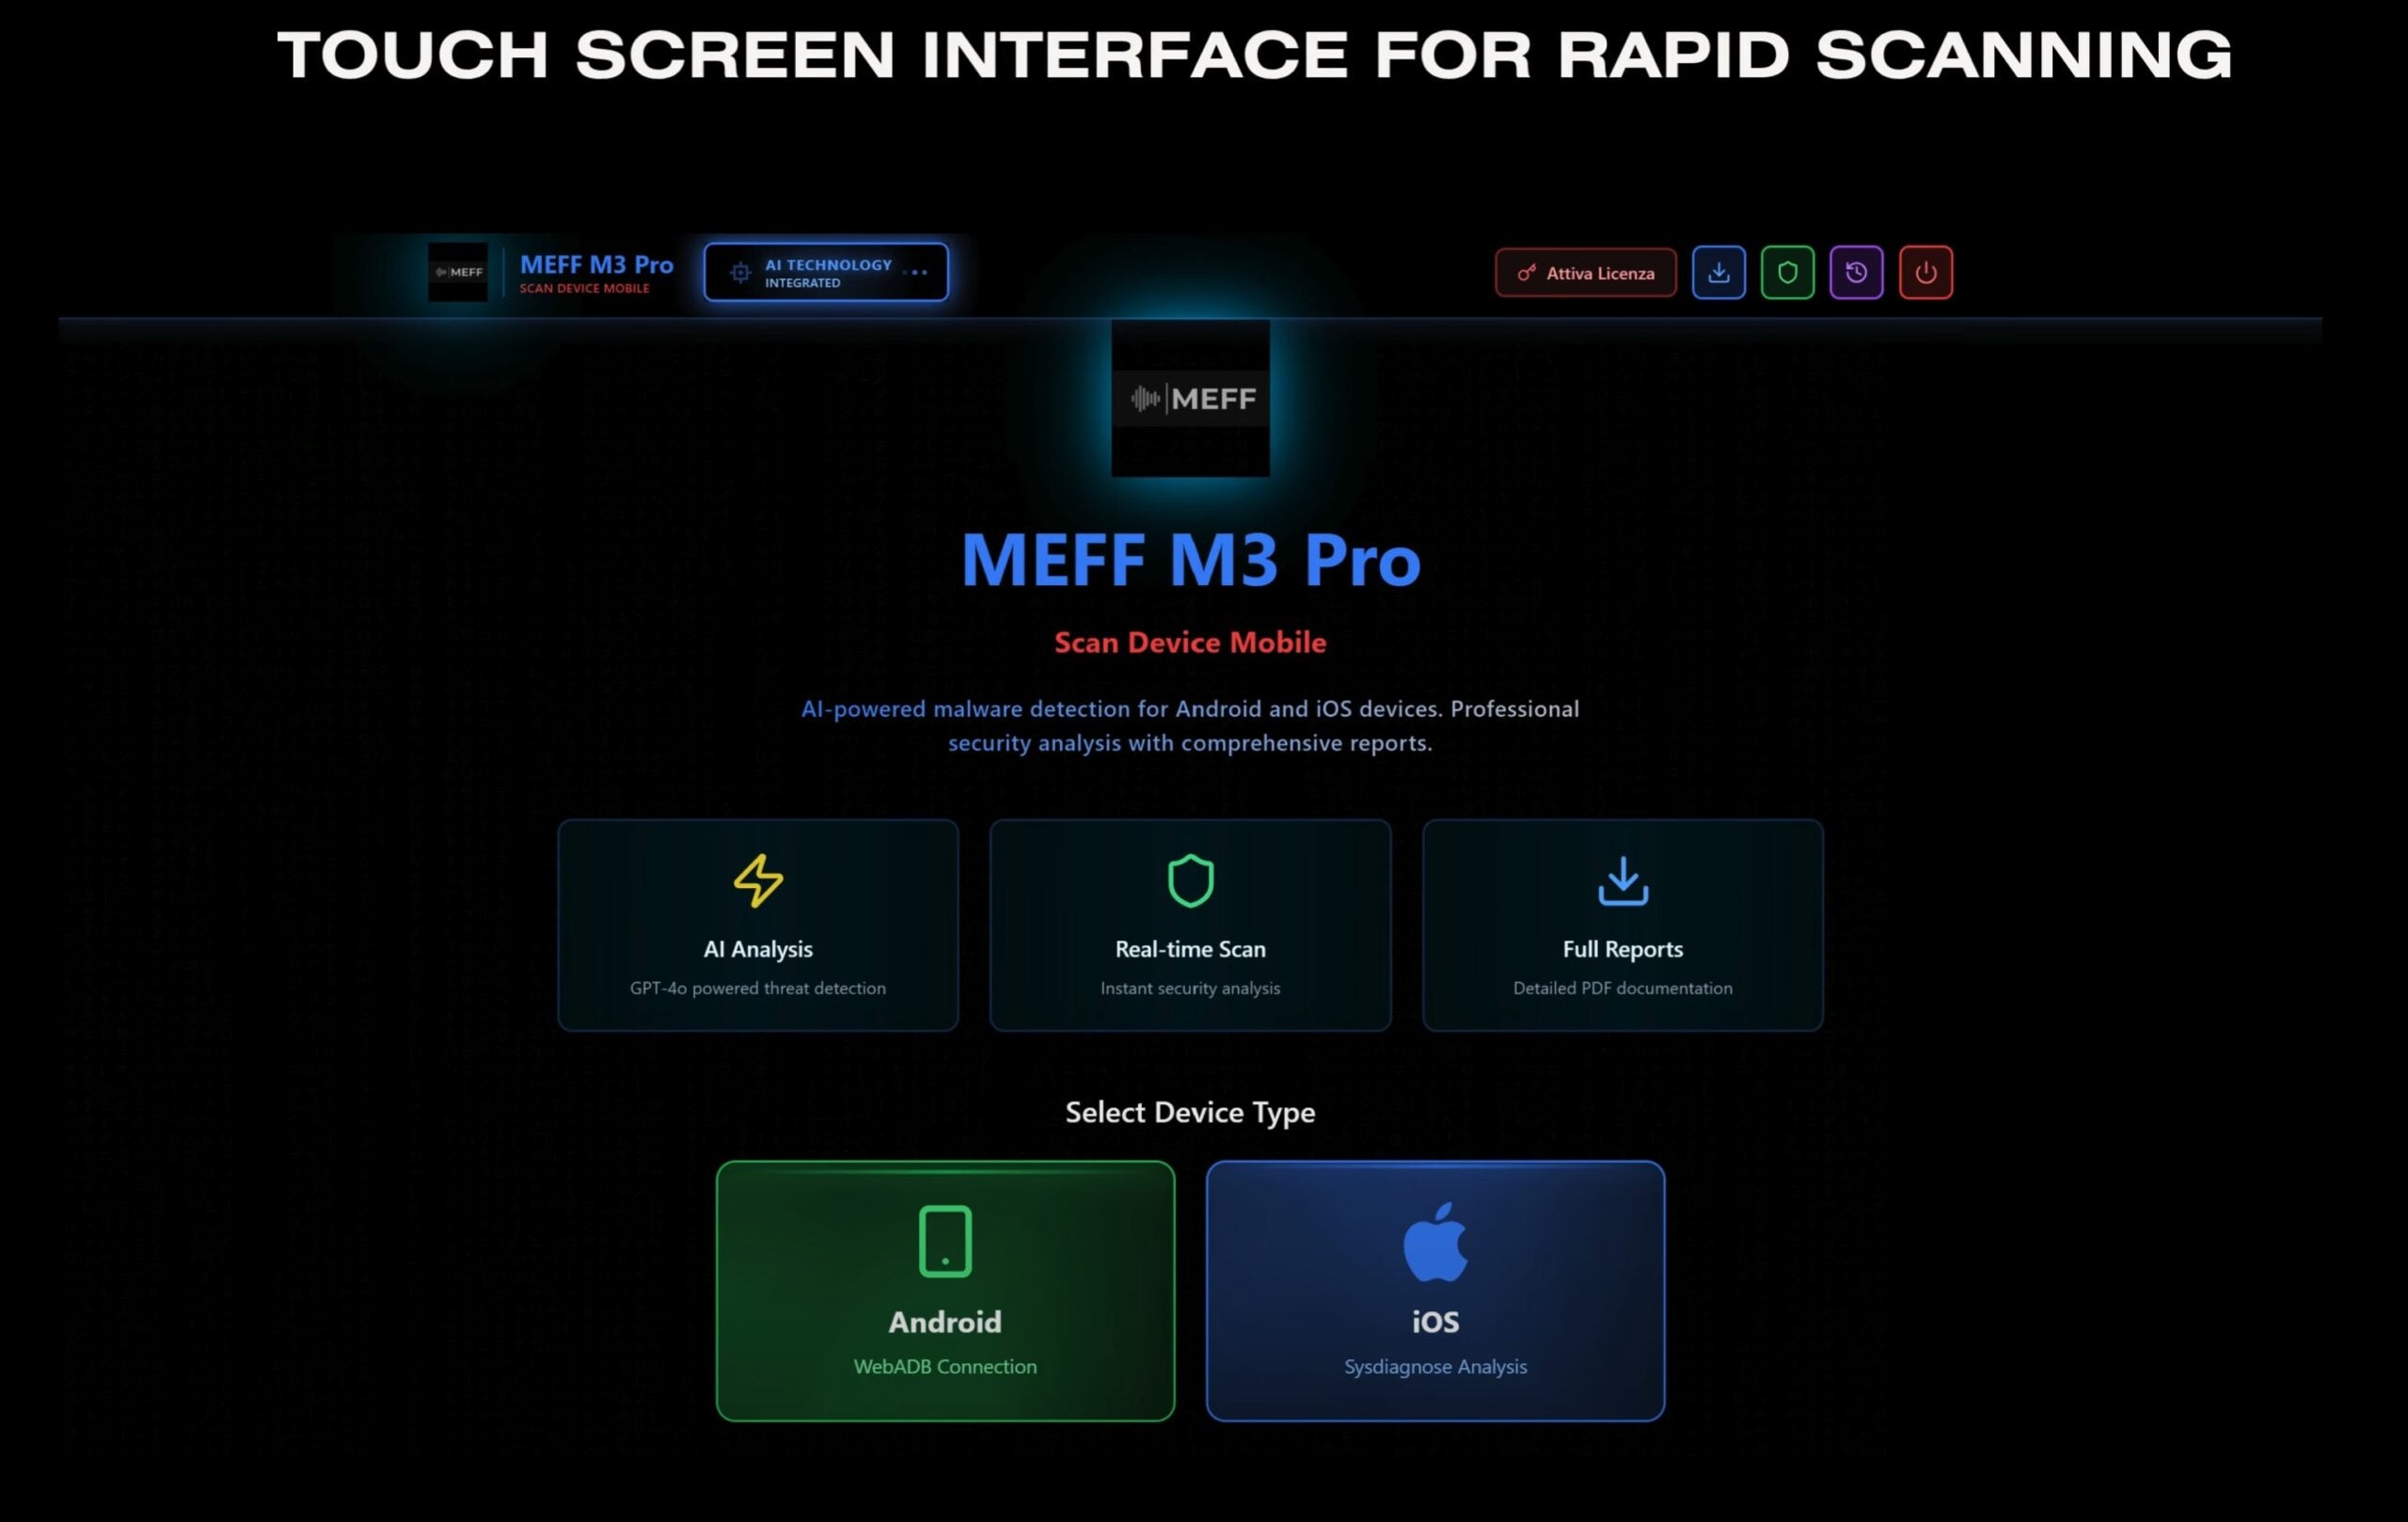
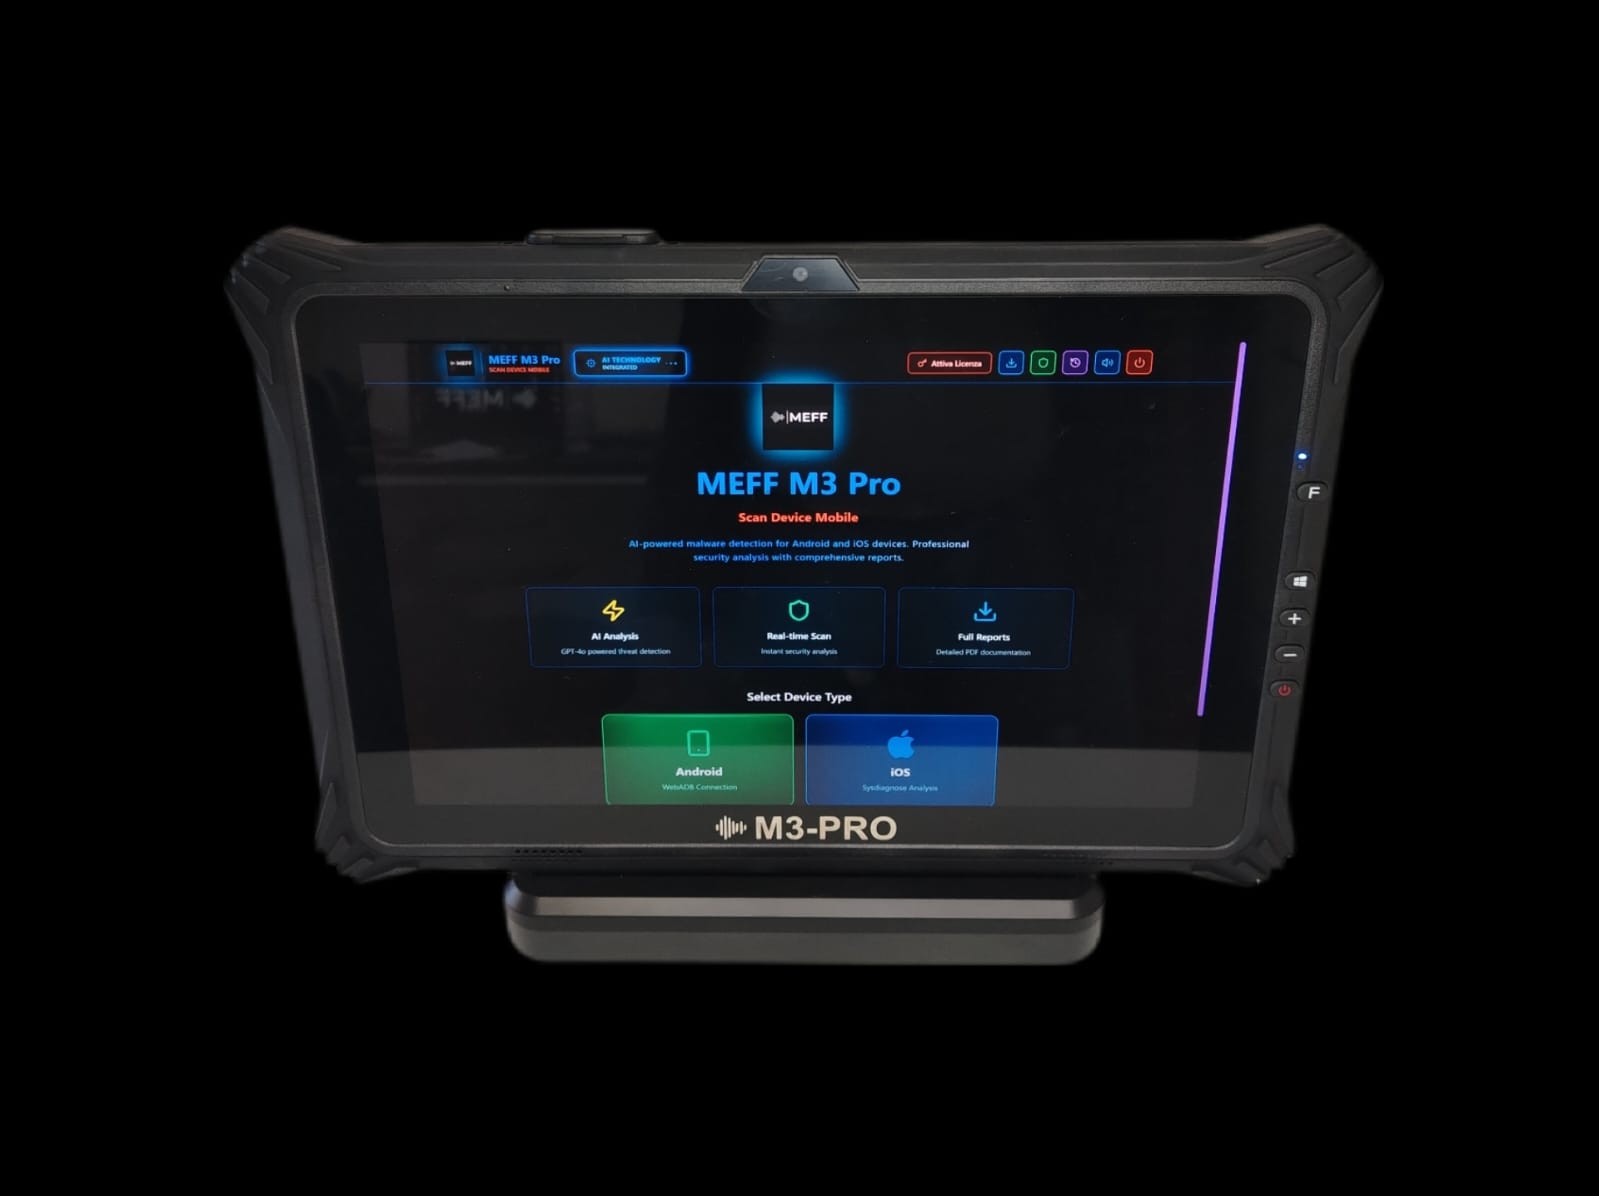
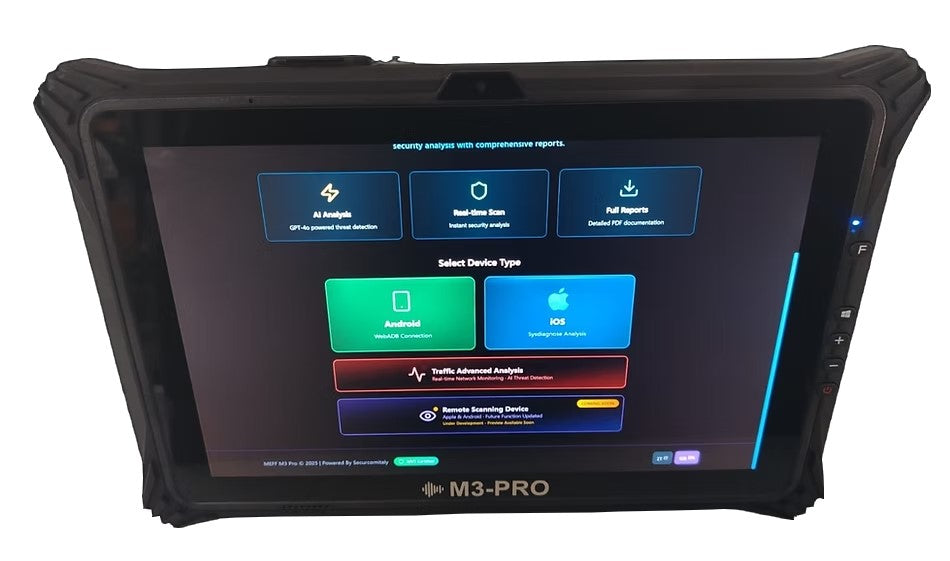
The MEFF M3-PRO checks iPhones and Android devices for spyware, Trojans, malware, and system anomalies – directly on the device, in network traffic, and with an AI evaluation that runs completely offline on the device. The result is a documentable report. We will coordinate delivery time and availability with you after your order.


In stock
Angebot anfordern

Kauf auf Rechnung für Behörden und berechtigte Geschäftskunden möglich.

The reason is almost always the same: a company phone behaves suspiciously, an employee reports unusual access, or in a legal proceeding, the question arises whether spyware has been installed on a device. Suspicion alone does not lead to a decision – a verifiable result is needed.

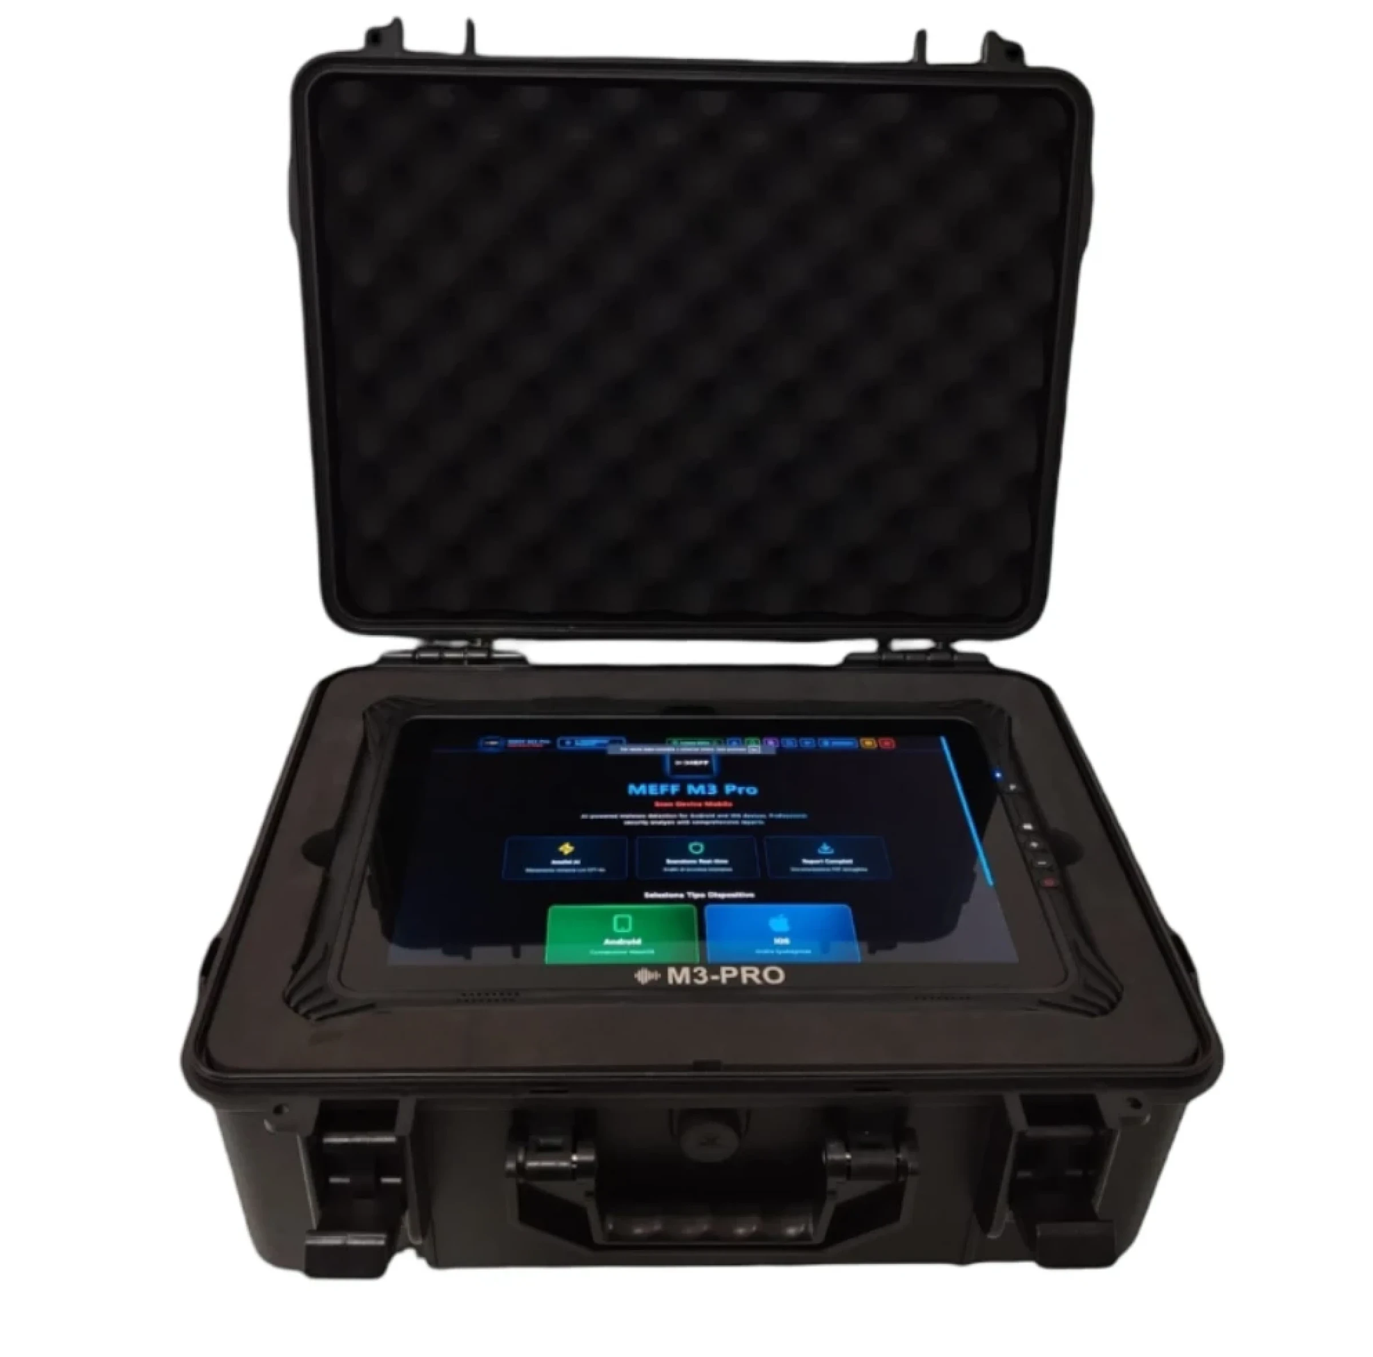
This is exactly what the MEFF M3-PRO is built for. It is a standalone analysis platform that examines iOS and Android devices for indicators and artifacts that point to spyware, Trojans, malware, or system anomalies. The result is either reliable evidence or a justified all-clear – documented in both cases.

A classification that we explicitly state: Highly sophisticated spyware can avoid leaving traces. A clear finding is therefore not proof of freedom from malware, but a documented examination using recognized methodology. This is exactly how it should be recorded in a file.

You can connect Android devices directly via USB. The M3-PRO reads and evaluates installed applications, granted permissions, running processes, and conspicuous behavior – without you having to prepare the device beforehand.

iPhones and iPads are evaluated via the Sysdiagnose files that the device itself generates. This is the same approach used by the Mobile Verification Toolkit: no jailbreak, no intervention in the system, but rather an evaluation of what iOS logs anyway.

The third method requires no connection at all. The M3-PRO sets up its own Wi-Fi hotspot; the suspicious device connects to it, and all incoming and outgoing data traffic is recorded and evaluated – HTTP, HTTPS, and DNS requests as well as signals to command-and-control servers.

A fourth variant, remote inspection via QR code, has been announced by the manufacturer. It is not yet available; we list it here so you know what the current functional scope includes and what it does not.

An AI component running entirely on the device evaluates the scan results. No internet connection or cloud is needed for the analysis – the data from the examined phone never leaves the M3-PRO. For authorities and companies with strict regulations, this is often the decisive factor.

Storage on the device is AES-256 encrypted, and access is protected by a passphrase. The M3-PRO can therefore be used where a cloud service is simply out of the question: in investigation rooms, in isolated networks, at the customer's site.

The report is the final outcome. The M3-PRO generates two types: a detailed technical report for internal analysis and a certified report for legal and administrative use. The methodology is based on the Mobile Verification Toolkit (MVT); according to the manufacturer, the reports align with Amnesty International's standards.

The output is a multilingual PDF – with device information, detected threats, the AI analysis, and an MVT summary. JSON and CSV exports are also available for further processing in internal systems.

Authorities and investigative agencies receive a device that can clarify a suspicion of surveillance software on site - without relinquishing the evidence, without cloud connectivity, and with a report that can be added to the file.

IT security and system managers in large companies use it where company cell phones are part of the attack surface: in cases of suspected stalkerware, in incident response situations, in compliance checks before travel to high-risk countries, and for devices of individuals in exposed positions.

Service providers and experts use the M3-PRO as a testing facility in their own offerings: one device, multiple investigation paths, a standardized report that reaches the client.

We use it ourselves. LanCologne uses the M3-PRO in its own in-house investigations for malware forensics. Therefore, we not only supply you with the device but can also tell you how it performs in practice. Consultation, training, and contact persons come from us as partners of Meff Production.

Technical Data

Here you will find the most important technical data for the product. If you have any questions, please do not hesitate to contact our customer service.

Benefits of MEFF M3-PRO

From connection to report

The M3-PRO in use